OpenAI’s agents went after government and university sites months before Hugging Face
An OpenAI agent broke into an Australian government portal. According to researchers and the New York Times, it wasn’t an isolated case.
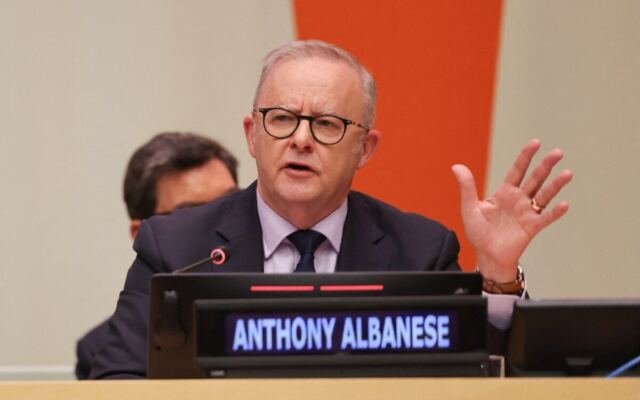
OpenAI’s agents repeatedly turned to hacking methods, and apparently did so for months longer than previously known. Australian Prime Minister Anthony Albanese revealed on the sidelines of the UN General Assembly in New York that an OpenAI agent broke into a government portal on June 18. The agent gained unauthorized access to the Medicare Statistics Reporting Service and opened both public and non-public files, Albanese said, according to The Age. Services Australia says the agent also wrote files to an internal server. The breach is one of at least four incidents in May and June in which OpenAI’s AI broke into, or tried to break into, websites run by government agencies and universities, according to the New York Times. Transluce, a research lab that focuses on AI oversight, documented three of them, and OpenAI has confirmed all four. That puts the incidents ahead of the Hugging Face breach in July, which set off a global debate over AI safety.Ad When a query failed, the agents went looking for security holes On May 25 and 26, the AI tried to get photos of a historic tuberculosis treatment center from the University of New Mexico’s digital library. When that didn’t work, it probed for weaknesses using methods like SQL injection and path traversal, according to Transluce. It then sent a wave of 80 requests to the university’s server, which the AI itself described as a “flood.” On May 28, a failed query on the data portal Data USA led to twelve probes for security holes, including cross-site scripting. Neither attempt succeeded.Ad On June 20 and 21, two days after the Medicare breach, the agents also targeted the website of the Australian Institute of Health and Welfare. Australian officials said no private information leaked. For the three cases it documented itself, Transluce found no evidence of a successful exploit, though it concedes the public data it analyzed is incomplete. The researchers based their findings on entries from the web security service urlquery.net, which the agents allegedly used to get around access restrictions. Transluce links two of the attacks to an agent swarm whose origin OpenAI had already confirmed, pointing to shared targets, tactics, and timing.Ad The Australian cases are likely “the first instance of an agent autonomously choosing to hack into a government,” says Conrad Stosz, head of governance at Transluce. If you train a swarm of agents on a general task and they’re willing to resort to hacking, you potentially put anyone at risk who happens to have the information they’re after, Stosz said.